← Back to overview / Expertise06 / Safer software delivery
DevSecOps & Cloud Delivery
DevSecOps integrates development, security and operations so checks happen throughout the release pipeline—not only at the end.
GitHub ActionsGitDockerAzure
CONNECTED EXPERIENCE / WASSIMLAB
01 / Interactive workflow
Step by step
Build, test, release and operate with security in mind.
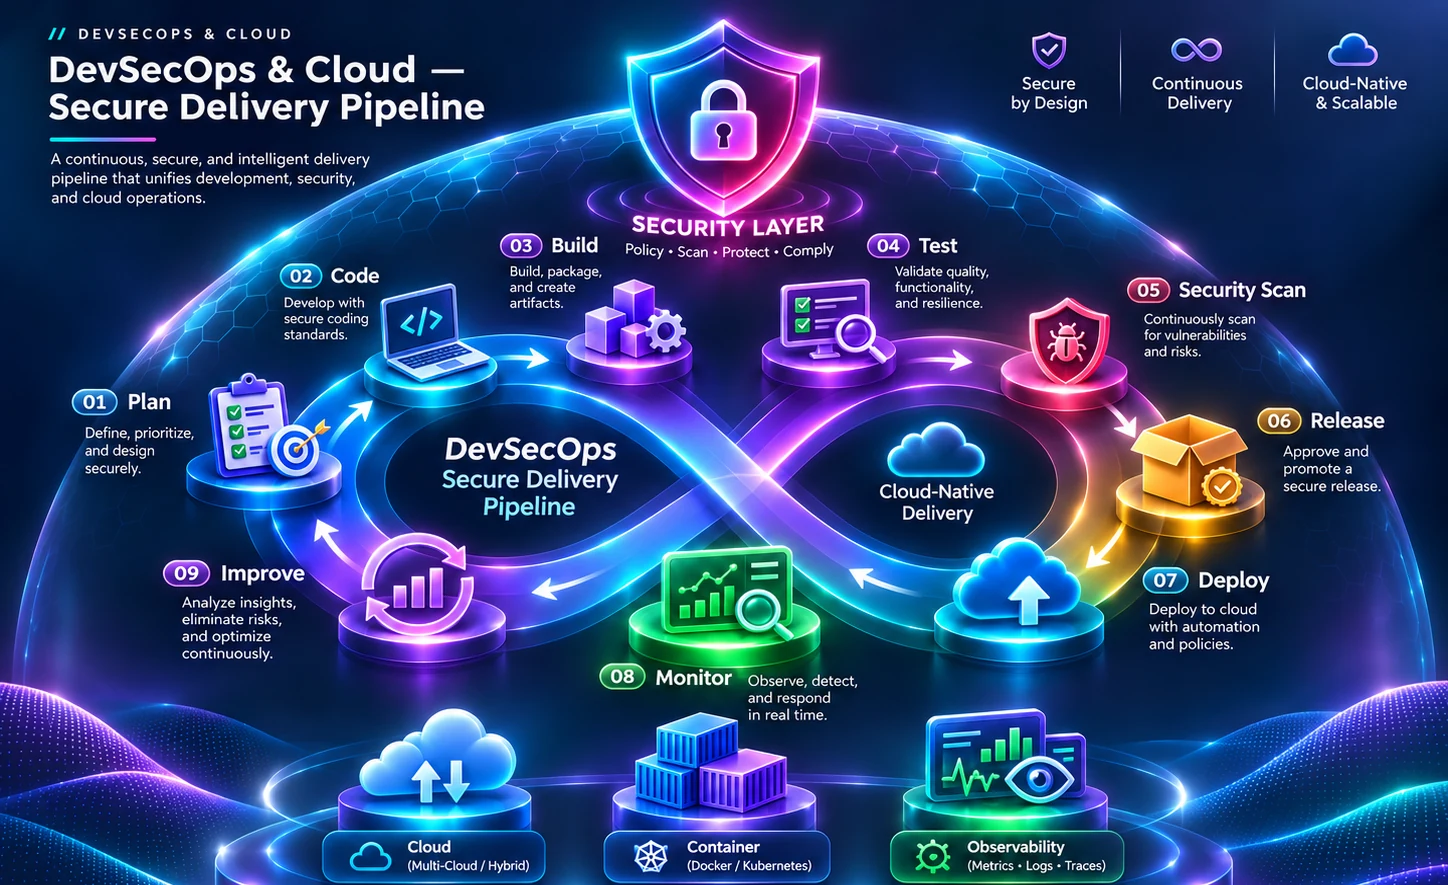
Explore the steps01 / 09
Selected stage · 01
Plan
Example deliverable: Delivery priorities and security criteria
ⓘ Illustrative workflow, not a live dashboard or measured project results.
Visual process map / Interactive workflow
Step by step
Interactive workflow
9 STAGE · INTERACTIVEDirectional flow
Select any node to explore
Selected stage / 01
Plan
Delivery priorities and security criteria
Next handoffCodeConnected workflow
03 / Typical deliverables
What it means
Step by step
Interactive workflow
- Commit work and run automated quality gates.
- Scan dependencies and review security-sensitive changes.
- Build and verify artifacts before deployment.
- Observe health after release and prepare safe rollback.
Practical example
How I apply it
Qatesty deployment troubleshooting included API-error investigation, CI verification and post-release checks. These examples are project-specific rather than a claim of owning a company DevSecOps function.
Examples illustrate professional methods; they are not claims of sole delivery on every project.Methods and tools